
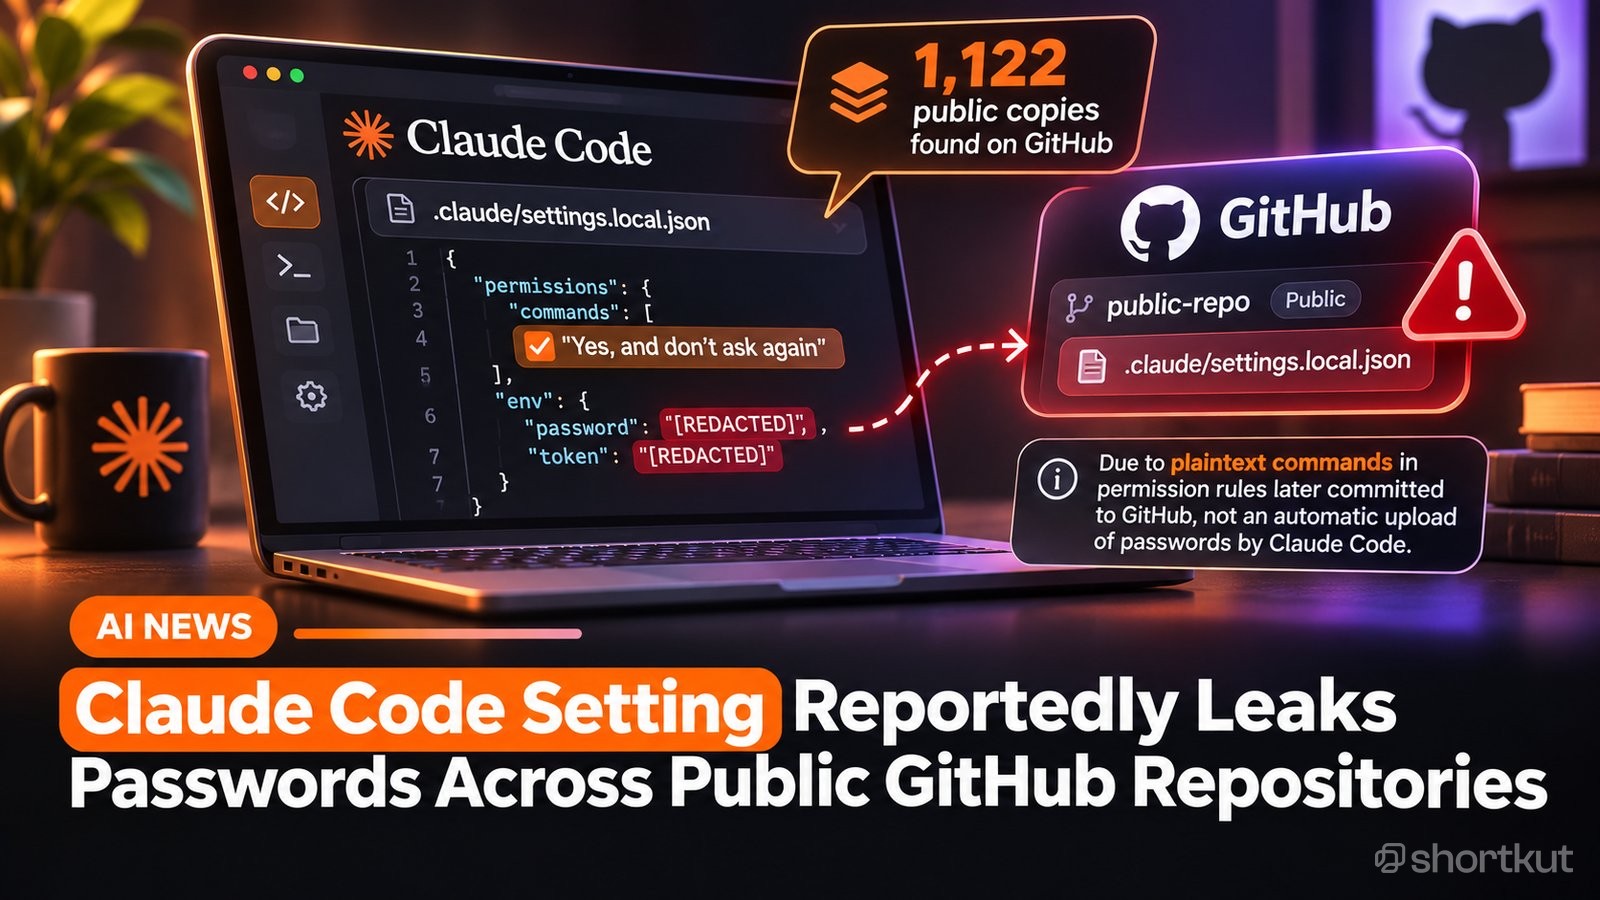
Security firm Apiiro published findings showing that passwords appeared across 1,122 public files hosted on GitHub. The leaks occurred when developers used Claude Code, an automated agent designed for software development tasks.
The exposure stems from the Don't Ask Again option in Claude Code. When users enable this setting to streamline their workflow, the assistant performs file modifications and repository actions without requesting confirmation for each step.
Without explicit confirmation prompts, sensitive authentication data and local configuration details can be committed directly to public source control systems.
Why it matters
Coding agents can significantly speed up project development, but removing manual oversight carries real risks. When safety prompts are turned off, AI assistants can easily treat private keys and passwords as standard project code.
Anyone relying on automated coding tools should maintain strict local protection. Developers must keep secrets inside secure environment files and use ignore lists so that assistants never expose private credentials to the web.
Try it yourself
Run this prompt with your AI assistant to generate a security checklist that prevents credentials from leaking into your repositories.
Review the following file structure and environment setup for my project: [paste your project file list or tech stack here]. Identify any potential risks where API keys, tokens, or passwords could accidentally get committed to public repositories. Provide a sample .gitignore file and a step-by-step checklist to ensure automated tools cannot read or publish my private secrets.
Comments