
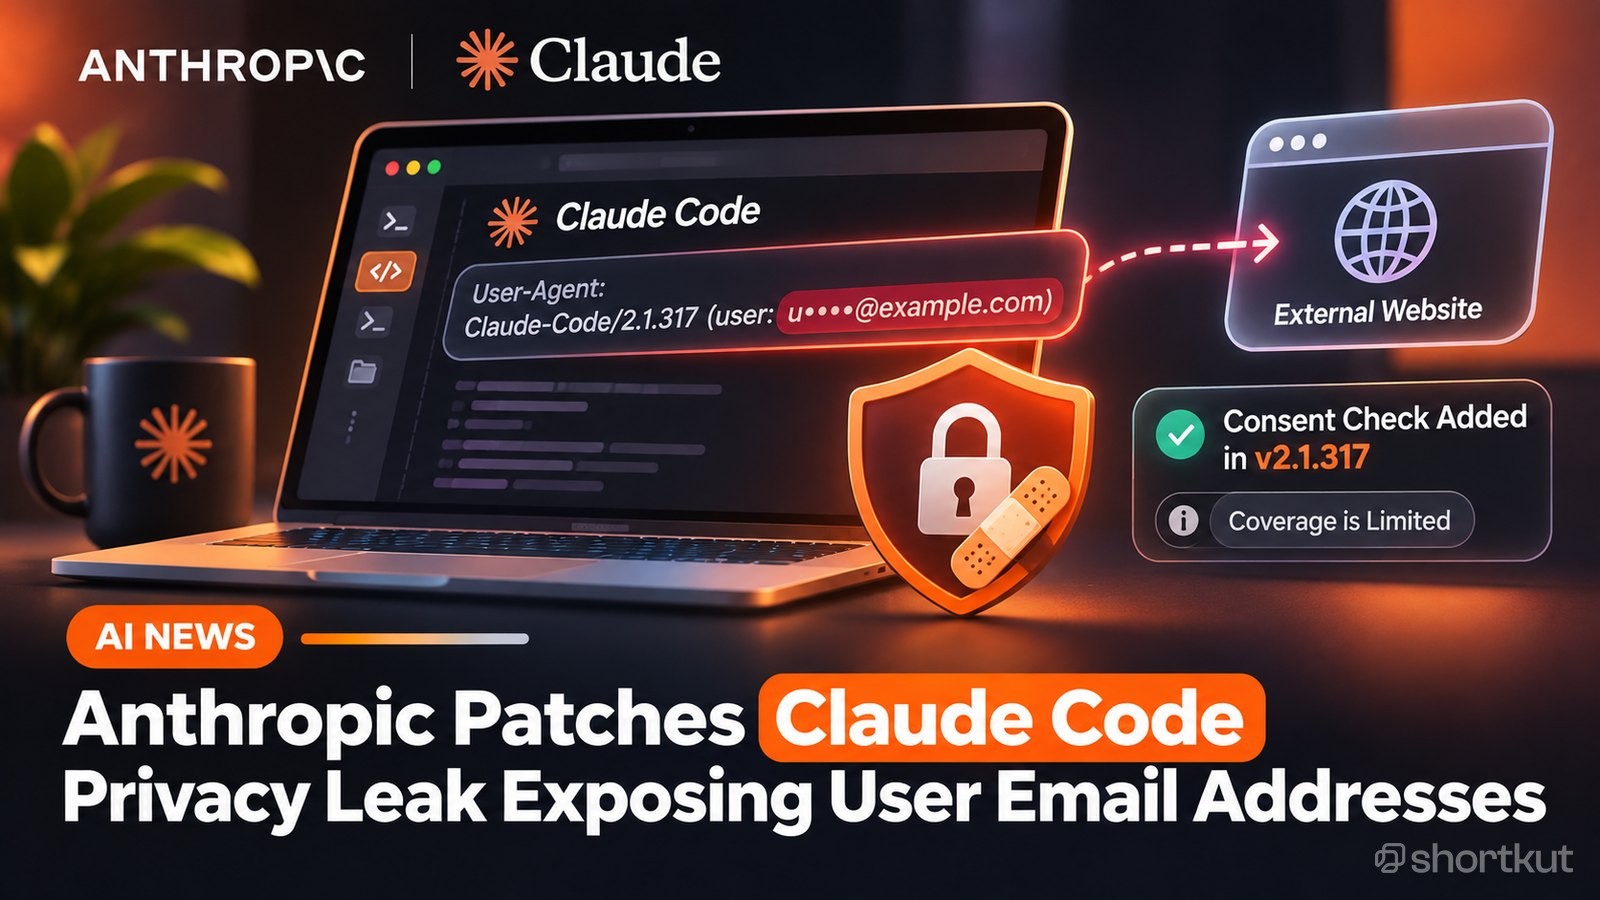
Users discovered that Claude Code shared their personal email addresses with third party websites during automated web searches. The software placed the account email address into the standard User Agent request header sent to external servers. One developer reported a flood of scam messages after external services gathered the exposed contact details.
Anthropic addressed the problem in version 2.1.317 by introducing a built in plugin called cc-plugin-privacy. This plugin is enabled by default to block personal email transmission across web queries. Users can inspect or manage the tool by running the plugins command in their terminal.
Community discussions noted that some platforms like Wikimedia and the SEC request contact information within the User Agent header. Even so, developers argued that exposing personal emails without explicit consent creates serious security risks and unwanted spam.
Why it matters
Coding agents routinely browse the web to fetch documentation, inspect repositories, or download packages. When developer tools send sensitive identity details over plain requests, creators face unwanted spam, tracking, and potential phishing attacks.
Anyone using automated terminal tools must verify their software versions. Keeping tools updated prevents background data leaks while preserving privacy during daily coding workflows.
Try it yourself
Check whether your AI coding tools or web scrapers expose personal identifiers during internet requests.
I am using an AI terminal agent to search the web for [describe task, such as fetching documentation or debugging code]. Act as a cybersecurity advisor. Explain what headers my system sends to web servers, identify what personal data could leak in the User Agent header, and give me a checklist to audit my network privacy settings.
Comments